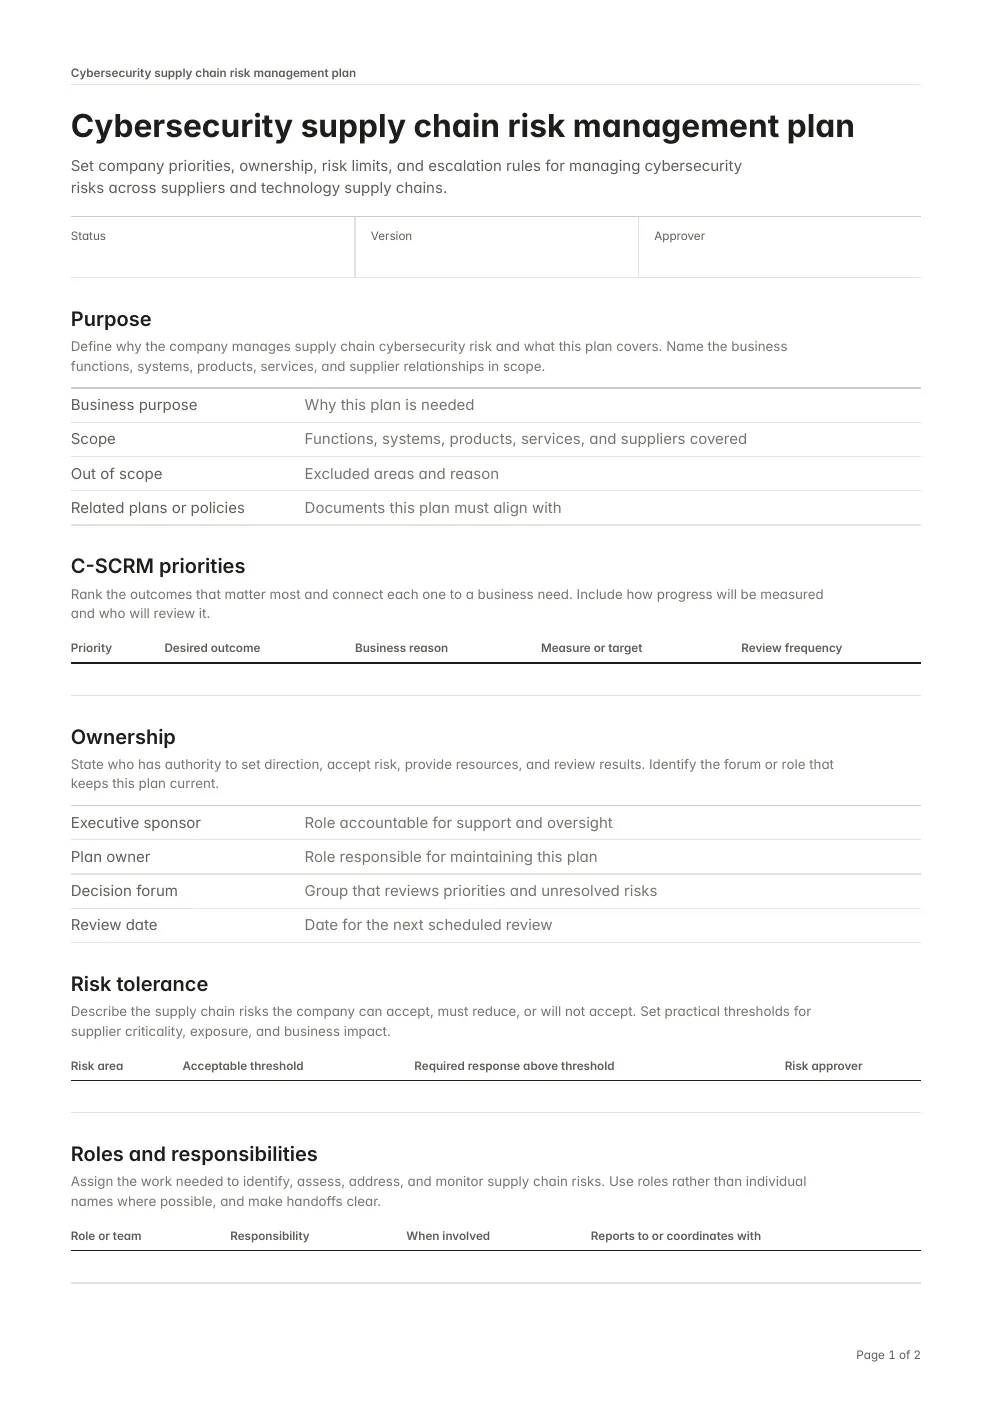
Set company priorities, ownership, risk limits, and escalation rules for managing cybersecurity risks across suppliers and technology supply chains. Use this plan to establish or refresh how the company manages cybersecurity risks tied to products, services, suppliers, and their supply chains.
PurposeDefine why the company manages supply chain cybersecurity risk and what this plan covers.
C-SCRM prioritiesRank the outcomes that matter most and connect each one to a business need.
OwnershipState who has authority to set direction, accept risk, provide resources, and review results.
Risk toleranceDescribe the supply chain risks the company can accept, must reduce, or will not accept.
Roles and responsibilitiesAssign the work needed to identify, assess, address, and monitor supply chain risks.
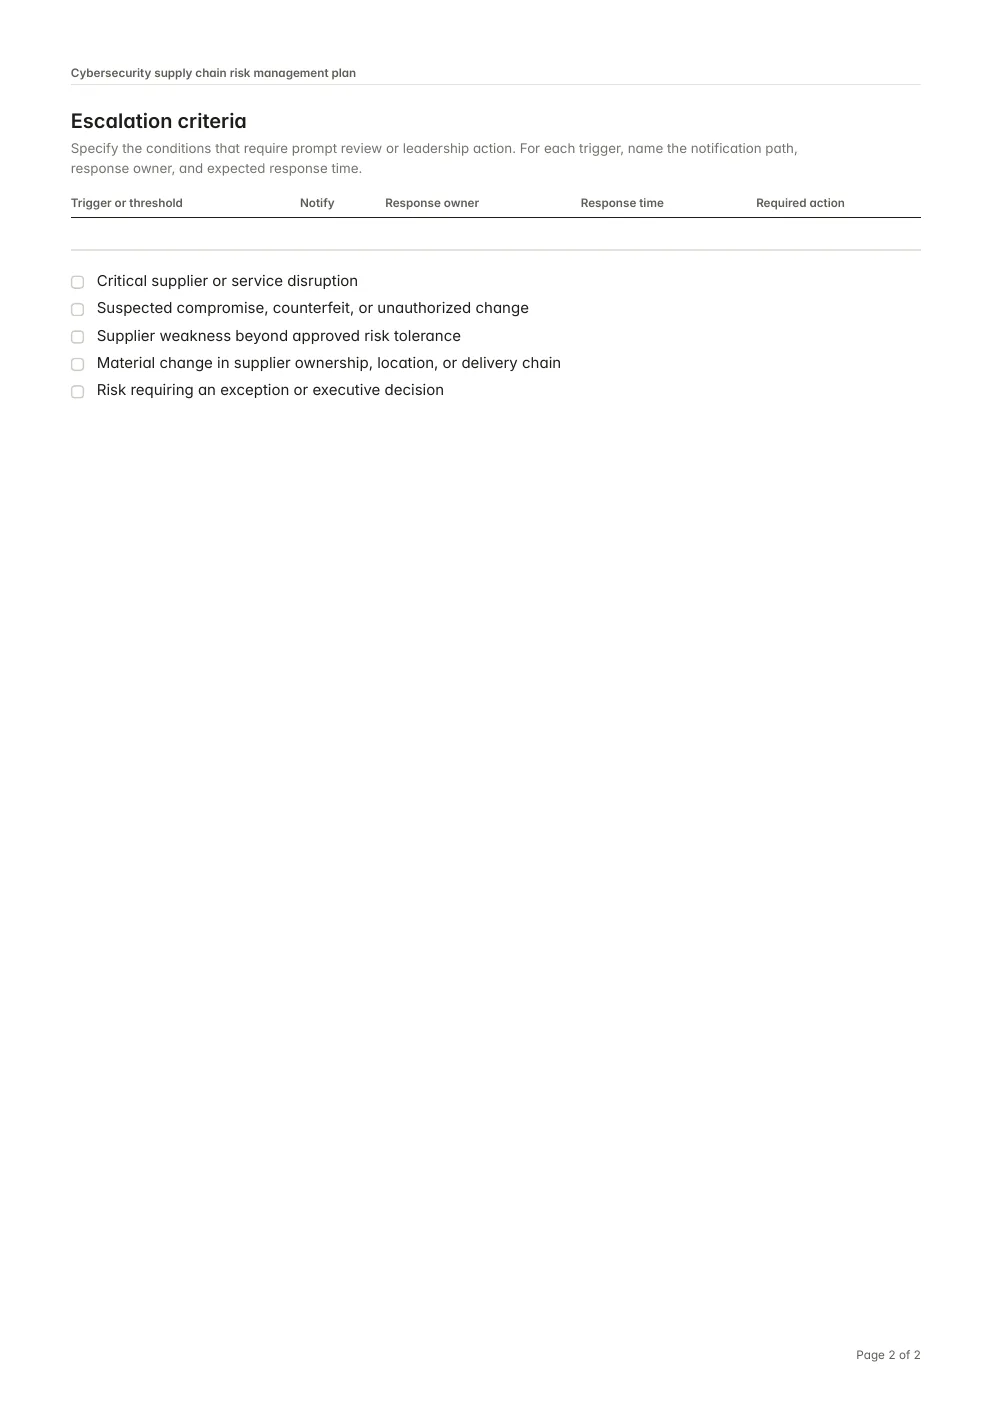
Escalation criteriaSpecify the conditions that require prompt review or leadership action.