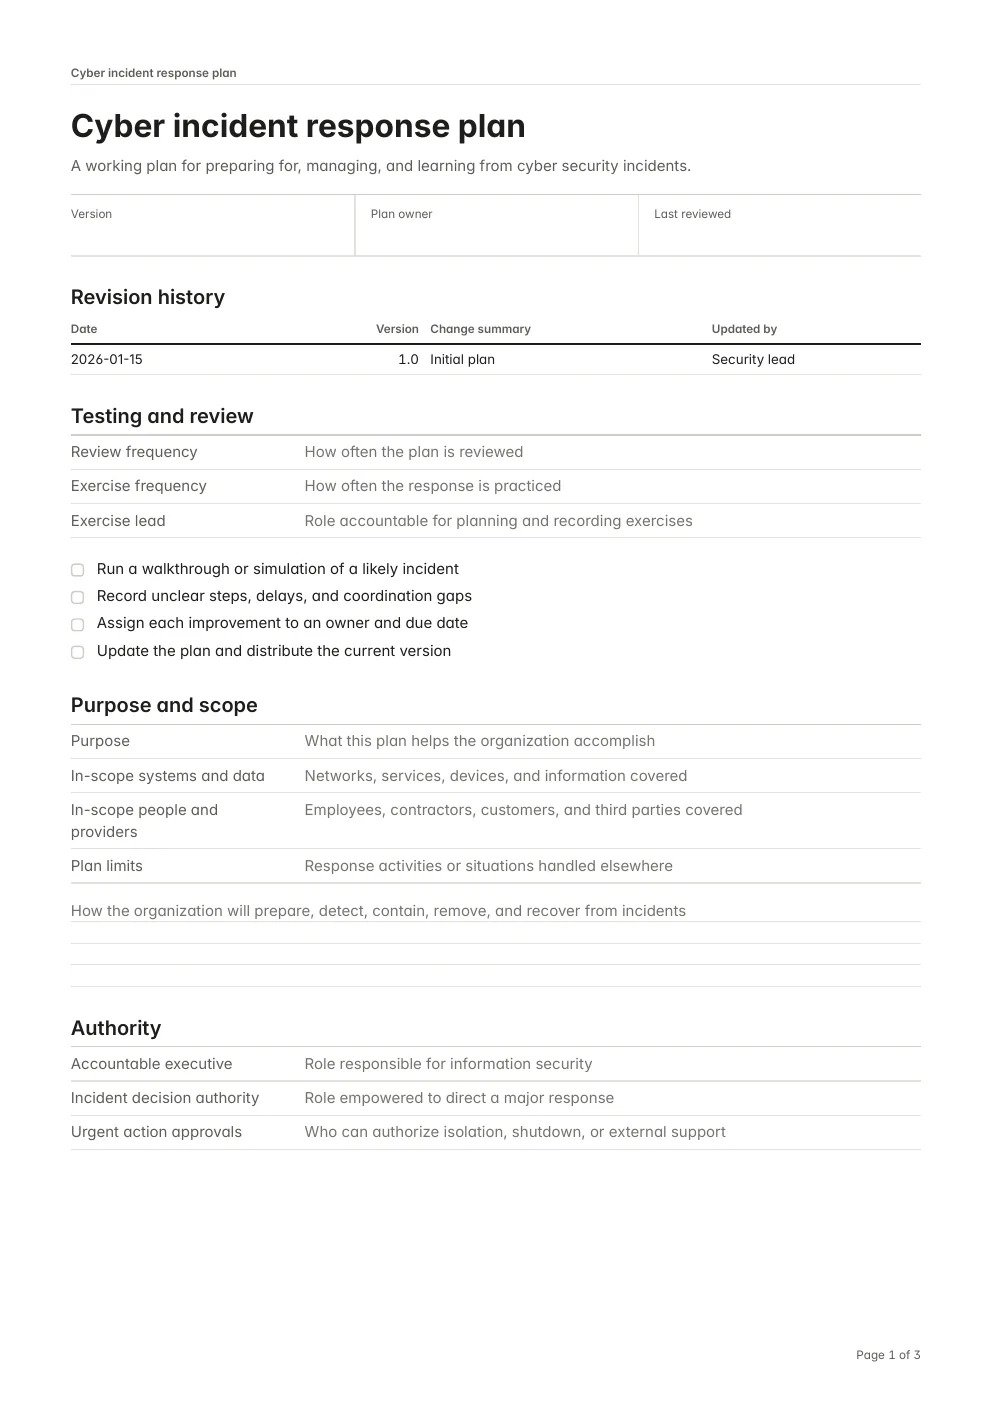
A working plan for preparing for, managing, and learning from cyber security incidents. Use this plan to assign response authority, guide incident handling, and keep the response team ready.
Revision historyLog each approved change so readers can see what changed, when, and who made it.
Testing and reviewSet a review schedule and exercise the plan with realistic scenarios.
Purpose and scopeExplain what the plan enables the organization to do and who or what it covers.
AuthorityName the role with overall accountability and the person who can direct response decisions during a serious incident.
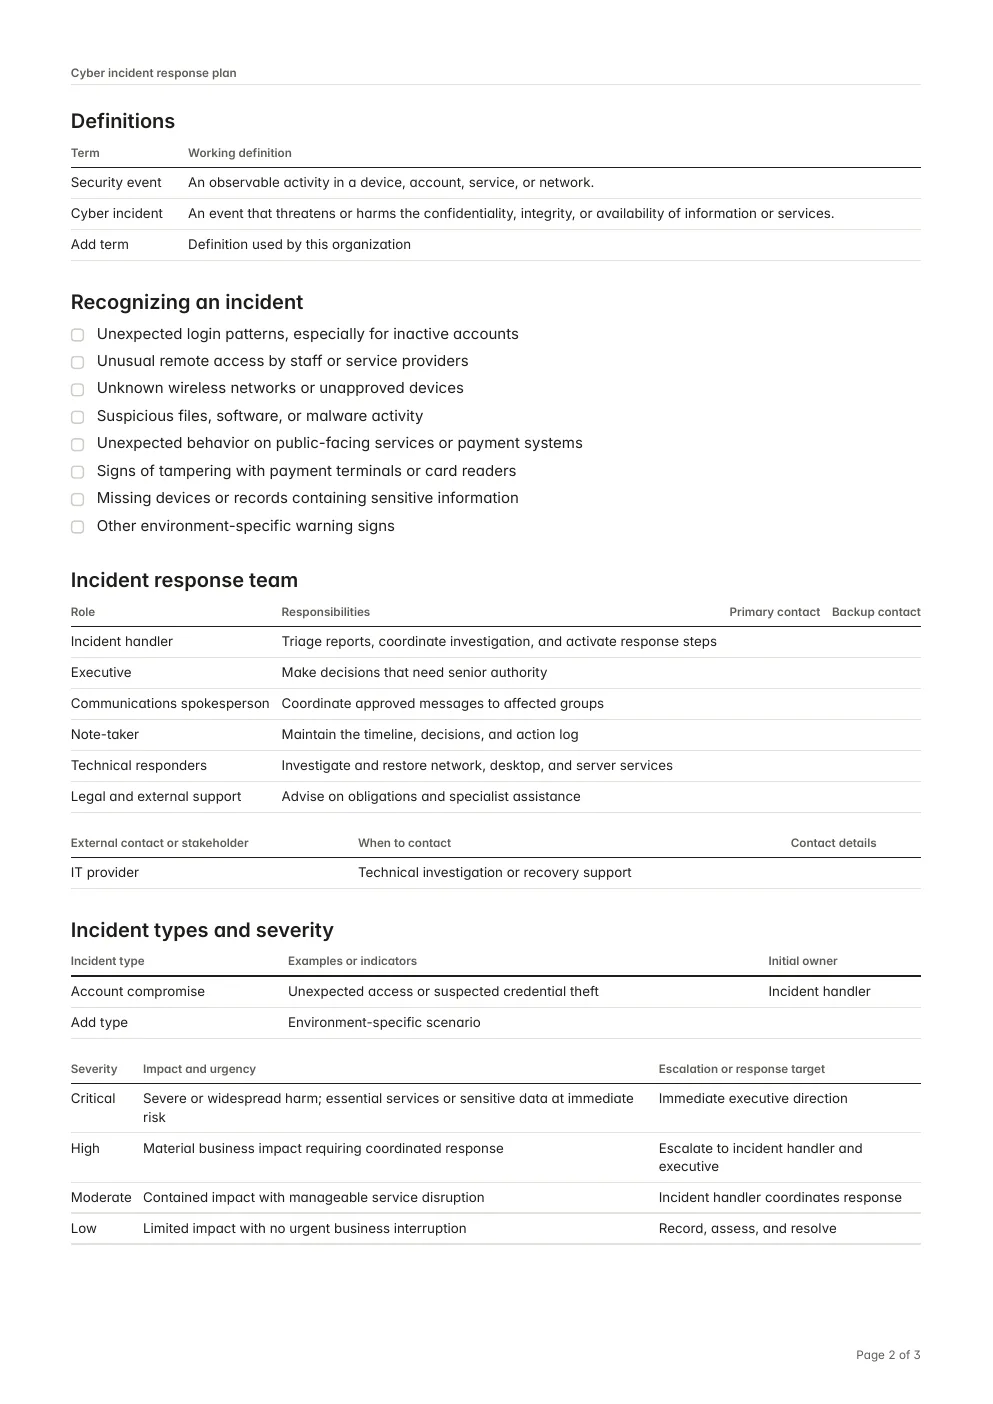
DefinitionsDefine terms the team needs to make consistent decisions.
Recognizing an incidentKeep the indicators that apply to your environment and add local warning signs.
Incident response teamAssign a lead, an executive decision maker, and a communications spokesperson.
Incident types and severityList the incident categories most relevant to the organization and define severity using business impact, urgency, and scope.
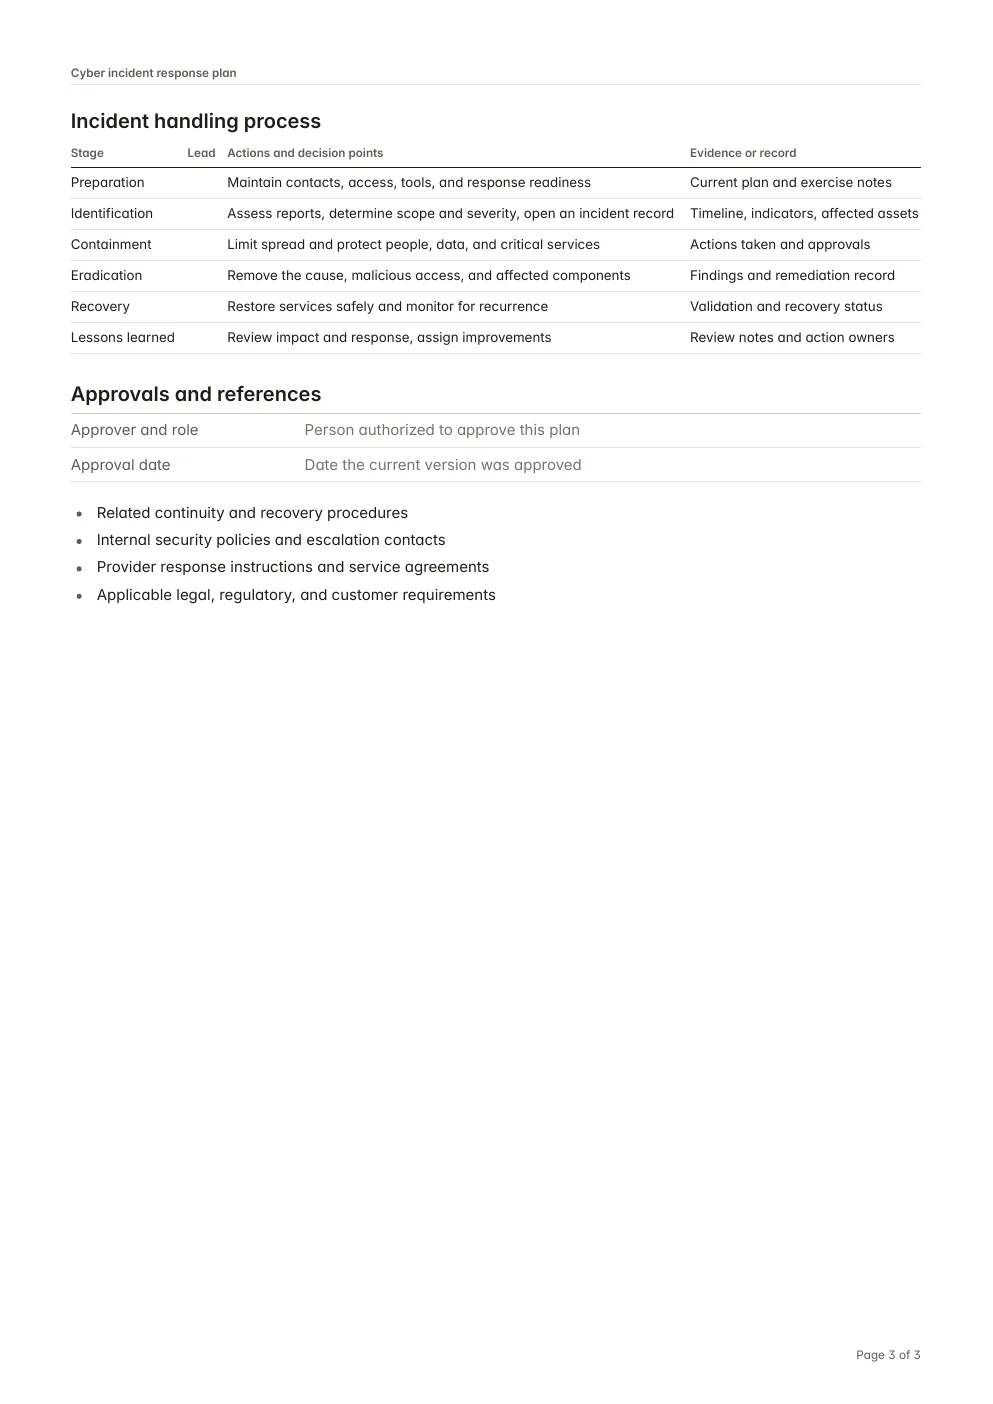
Incident handling processUse these stages to coordinate the response from preparation through follow-up.
Approvals and referencesRecord who approved the current plan and list the internal procedures, provider instructions, and obligations responders may need to consult.